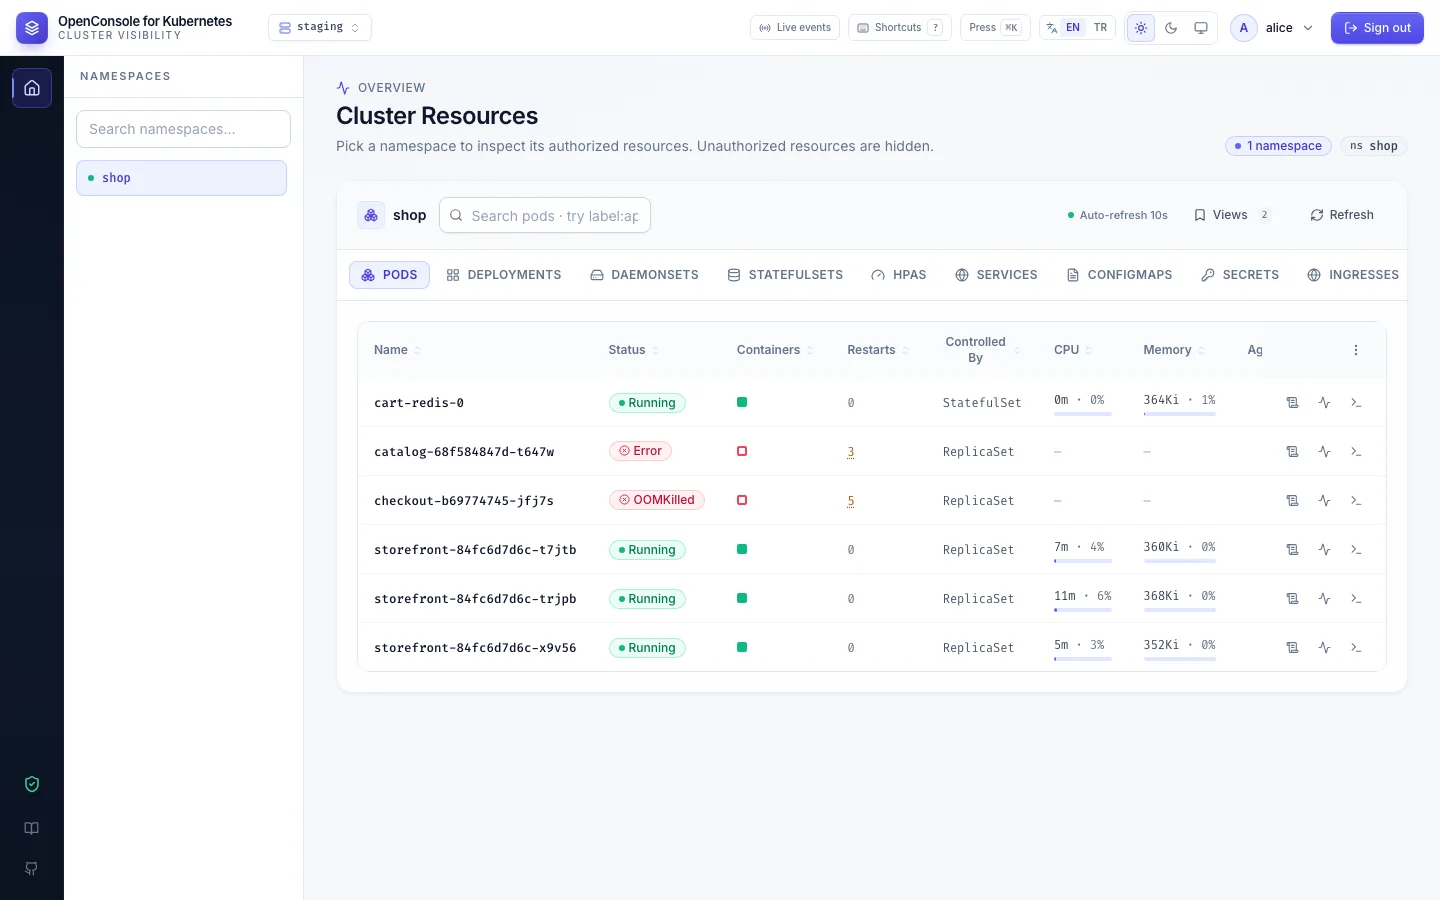
Access granted in the app
Users, groups and roles grant actions per cluster and namespace. People never get Kubernetes credentials; the console reads each cluster with one ServiceAccount. Local, LDAP and Azure AD accounts.
Every action audited
Reads and writes, sign-ins, denied calls: one structured event each, in the app and on stdout (ECS for Elastic). Pod shells are recorded and can be replayed.
Why a pod is failing
Pod status as kubectl prints it, the last exit code explained, the log before the restart, CPU and memory against limits, restart history, an overview and a node screen for admins.
An API for scripts and agents
Scoped API keys that never exceed their owner, an OpenAPI 3.1 description, logs and one command over plain REST. Claude Code or Cursor work with the same rules as people.